Documentation review: 26 October 2026. The incident described in the original article is historical. Its two suggested workarounds should not be treated as current general guidance.
Microsoft now documents a specific behaviour when the combined number of IP ranges in location policies exceeds 5,000: real-time enforcement of location changes is unavailable and Entra issues a one-hour CAE token. Other supported critical events continue to be evaluated.
That distinction matters. A location-policy limitation does not mean that every benefit of CAE is lost, and disabling CAE across the tenant should not be the default response.
When investigating a similar incident, first compare the actual tenant configuration, affected client and resource against the current documentation. Capture the sign-in evidence and reproduce the failure with a limited test group before changing an enforced policy.
Source: Microsoft: Continuous access evaluation, including named-location limitations.
Original field report — historical context
The original wording and screenshots below document the behaviour observed at the time.
We broke the Matrix:
I love the Idea behind Continues Access Evaluation aka (CAE) and we have it been using for quite a while. Because it improves the situation on Apps that support it around TOCTOU significant.
Now I came across a Problem around Named Locations:
First what is CAE:
CAE introduces real-time enforcement of account lifecycle events and policies, including:
- Account revocation
- Account disablement/deletion
- Password change
- User location change
- User risk increase
So let’s go closer to the “User location change” this is usually based on the IP of Users and that is where Named Location come into play.
First have a closer look on Named Location conditions:
- Configure up to 195 named locations
- Configure up to 2000 IP ranges per named location
- Both IPv4 and IPv6 ranges are supported
- Private IP ranges cannot be configured
Where is now the problem:
We got tasked with blocking around ±5000 IP Ranges within CIDR format due to some geo political topics.
First we actually played around with bumping 5000 IP Ranges into one Named Location which worked to our supprise.
But now come to the Issue.
We splitted the ±5250 IP’s in 3 Named Location with each ±1750. Remember the supported scenario statement from above.
We were testing this in Report Only Mode for a long time and had exactly 0 Problems with it.
So we activated the policy, and everything was still working as expected. After some time we got reports from Windows Outlook Clients having issues to download the Offline Address Book. We first didn’t see the conincidence because everything else continued to work just normal.
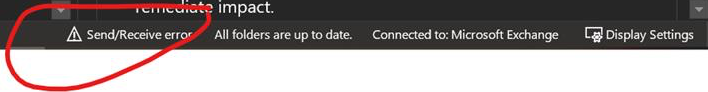
Now at the end it turned out the Workload Exchange Online has issues with large block lists in combination with CAE.
Currently you have only 2 choices:
- Turn off CAE for the complete Tenant
- Move the Policy to Report Only and have an alert when the policy hits
Imported from frank.cloud. The original page did not display a publication date.